Open for Part-Time Remote Projects & Full-Time Roles

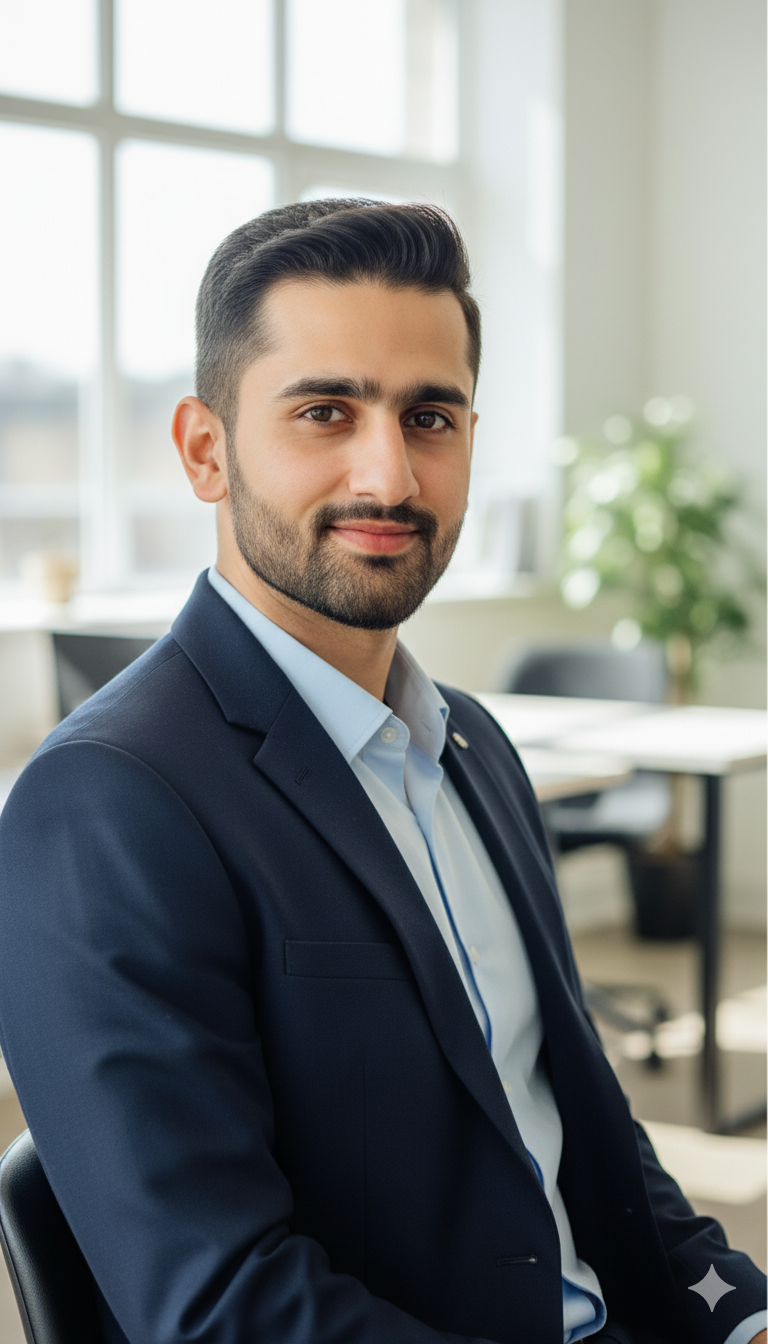
Muhammad Mohsin Ashraf

> Senior Security Expert & SOC Team Lead

Cybersecurity Engineer with 5+ years of experience designing enterprise SIEM/XDR platforms, orchestrating multi-customer SOC operations, and engineering advanced threat detections across Malaysia, UAE, Saudi Arabia, and Pakistan. Master's in Information Security from NUST.

Muhammad Mohsin Ashraf
๐Ÿ›ก๏ธ
5+ Years
SOC & SIEM Engineering
๐Ÿ†
CEH v13
ISO 27001 Lead Auditor

5+

Years Security Operations

7+

National & Enterprise Deployments

10+

Professional Certifications

500+

Engineers & Students Mentored

End-to-End Cyber Defense Engineering

Available for consulting, architecture, and hands-on execution for startups, enterprises, and MSSPs.

๐ŸŒ

SIEM & XDR Platform Architecture

End-to-end design, deployment, and optimization of enterprise SIEM platforms. Ingestion pipelines, log normalization (ECS), parsing rules, and role-based analyst dashboards.

Elastic Security Wazuh Logstash Kibana KQL
๐Ÿฆ…

EDR Operations & Incident Triage

Certified CrowdStrike Falcon Hunter with extensive expertise in endpoint protection, triage workflows, root cause analysis, containment, and multi-tenant SOC delivery.

CrowdStrike Falcon MS Defender Incident Triage Host Containment
๐ŸŽฏ

Detection Engineering & Decoders

Crafting actionable, high-fidelity correlation rules mapped to MITRE ATT&CK framework to significantly cut false-positive alert fatigue and detect stealth intrusions.

MITRE ATT&CK Custom Decoders Sigma Rules Alert Tuning
โšก

SOAR & Workflow Automation

Building automated playbooks for enrichment, alert deduplication, and immediate threat mitigation using open-source & commercial SOAR frameworks and scripts.

TheHive Cortex DFIR-IRIS n8n Python & Bash
๐Ÿ”

Vulnerability Assessment & Hardening

Comprehensive external and internal vulnerability scanning, risk evaluation, compliance readiness (ISO 27001), and remediation advisories for critical assets.

OpenVAS Nmap Wireshark Barracuda WAF ISO 27001
๐Ÿ‘ฅ

SOC Team Leadership & MSSP Handover

Leading tier 1-3 security operations teams, establishing standard operating procedures (SOPs), conducting training, and managing multi-customer security delivery.

Team Lead SOP Creation Operational Handover KPI Tracking

Mission-Critical Security Projects

Selected high-impact enterprise, telecom, and national-level cybersecurity platform rollouts.

๐Ÿ“ Malaysia Government

Ministry of Transport โ€” SOC Support & SIEM/XDR

Designed and deployed a comprehensive SIEM & XDR platform with ongoing SOC operations for the Ministry of Transport. Onboarded Windows, Linux, firewall, and network telemetry with MITRE ATT&CK detection mapping.

Key Outcome: Real-time visibility across critical national transit systems and consolidated executive dashboarding.
SIEM/XDR MITRE ATT&CK Linux & Windows Firewall Ingestion
๐Ÿ“ Malaysia National Security

Visa & Immigration โ€” SIEM, XDR & Continuous SOC

Implemented an end-to-end SIEM & XDR solution with continuous SOC support for a national visa and immigration environment. Rolled out managed endpoint agents and tuned custom detection rules.

Key Outcome: Accelerated containment of endpoint threats and established high-fidelity incident triage procedures.
Endpoint Security Detection Tuning Incident Response
๐Ÿ“ United Arab Emirates Enterprise MSSP

Depth Defense โ€” XDR & SOAR Automated Containment

Delivered an integrated XDR and SOAR deployment, configuring automated endpoint response workflows and threat isolation to drastically reduce Mean Time to Respond (MTTR).

Key Outcome: Automated threat containment playbooks reducing response time from hours to seconds.
SOAR TheHive Cortex Automated Isolation
๐Ÿ“ Pakistan Tier-1 Telecom

Redtone Telecom โ€” SOC Support & SIEM/XDR

Provided 24/7 SOC operations support and SIEM & XDR deployment for a tier-1 telecom carrier, delivering continuous monitoring, triage, and detection engineering across critical telecom nodes.

Key Outcome: Robust 24/7 monitoring covering core infrastructure against distributed volumetric and targeted attacks.
Telecom SOC Network Flow Detection Engineering
๐Ÿ“ Saudi Arabia Cloud Enterprise

Optiva โ€” SIEM & XDR Telemetry Integration

Delivered a complete SIEM & XDR rollout for Optiva, unifying endpoint, server, and network telemetry with automated alert triage and threat intelligence enrichment.

Key Outcome: Consolidated multi-cloud & on-prem telemetry into a unified single-pane-of-glass monitoring view.
Alert Triage Threat Intel Elasticsearch
๐Ÿ“ Malaysia Higher Education

University of Malaya โ€” SIEM Ingest & Normalization

Built high-throughput log ingestion pipelines to normalize heterogeneous logs into ECS format and authored role-based operational dashboards for continuous security monitoring.

Key Outcome: Scalable ingestion architecture parsing millions of daily events with zero data loss.
Logstash ECS Normalization Kibana Dashboards
Professional Experience

5+ years driving security operations, SOC leadership, and platform engineering.

Senior Security Expert โ€” Team Lead

IOTA Solutions โ€ข Pakistan
Feb 2025 โ€“ Present
  • Lead and direct the security operations team, assigning investigation priorities and handling critical incidents.
  • Design, architect, and deploy customer-specific SIEM and XDR platforms from kickoff to operational handover.
  • Oversee CrowdStrike and endpoint security workflows, developing correlation logic and custom parsing mechanisms.
  • Perform continuous vulnerability assessments and advise enterprise clients on risk remediation strategies.

Cybersecurity Engineer

Etika Info Sdn Bhd โ€ข Malaysia
Jul 2023 โ€“ Feb 2025
  • Analyzed security events and incidents generated by SIEM and XDR platforms, producing technical root-cause reports.
  • Operationalized CrowdStrike Falcon EDR alerts, designing response playbooks and integrating endpoint telemetry into the SOC.
  • Fine-tuned correlation rules and decoders to maximize detection accuracy and eliminate false positive noise.
  • Conducted external and internal vulnerability assessments with OpenVAS and Kali Linux tools.

Consultant SecOps

IOTA Solutions โ€ข Pakistan
Aug 2021 โ€“ Dec 2023
  • Administered and fine-tuned SIEM solutions, firewall appliances, and log aggregation engines.
  • Analyzed network flow data for anomalies and swiftly coordinated containment of malicious indicators.
  • Awarded the Best Performance Award for exceptional service delivery and customer platform stability.

Certifications & Academic Honors

Recognized industry credentials backed by formal cybersecurity research degrees.

๐ŸŽ–๏ธ

Certified Ethical Hacker (CEH v13)

EC-Council

๐Ÿ“œ

ISO/IEC 27001:2022 Lead Auditor

Mastermind Verification

๐Ÿฆ…

CrowdStrike Certified Falcon Hunter

CrowdStrike University

โ˜๏ธ

AWS Certified Cloud Practitioner

Amazon Web Services

๐Ÿ›ก๏ธ

Certified in Cybersecurity (CC)

ISC2

๐ŸŒ

Certified Network Security Practitioner

CNSP

๐Ÿงฑ

Barracuda Web Application Firewall

WAF01 Foundation

๐Ÿ

Python & OS Automation

Google Professional Certification

๐Ÿ†

Best Performance Award

IOTA Solutions

Master's in Information Security (MS-IS)
National University of Sciences & Technology (NUST) โ€ข 2021 โ€“ 2024
CGPA: 3.5 / 4.0

Thesis: Investigation of Security-Related Routing Issues in IoT Networks. Advanced coursework in Network Security, Cryptography, Cloud Security, and Vulnerability Exploitation.

BS in Computer Systems Engineering
Bahauddin Zakariya University (BZU) Multan โ€ข 2017 โ€“ 2021
CGPA: 3.85 / 4.0

Comprehensive grounding in Computer Architecture, Operating Systems, Networking, Data Structures, and Applied Network Defense.

๐Ÿ›ก๏ธ

Mohsin's AI Ambassador

Powered by Gemini
๐Ÿ‘‹ Hi! I am Mohsin's AI Security Ambassador. Ask me anything about Mohsin's 5+ years in SIEM/XDR architecture, CrowdStrike EDR, national defense deployments, or his availability for remote projects and full-time roles!